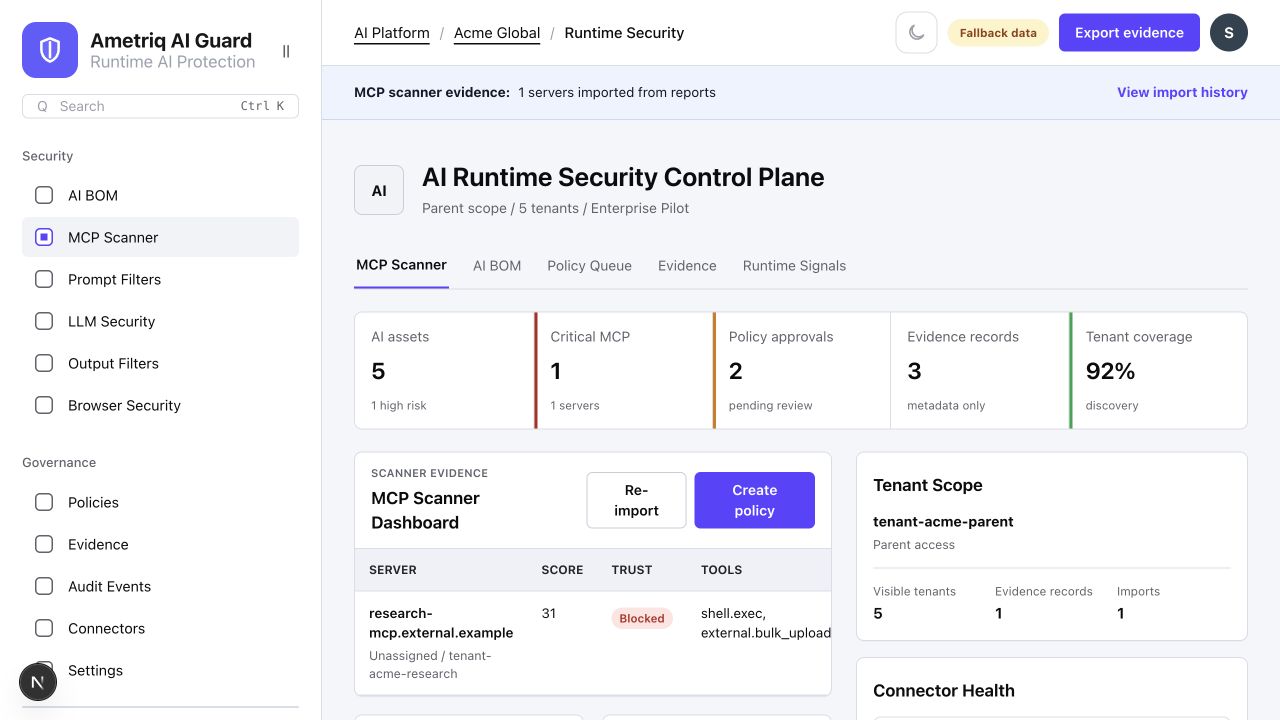
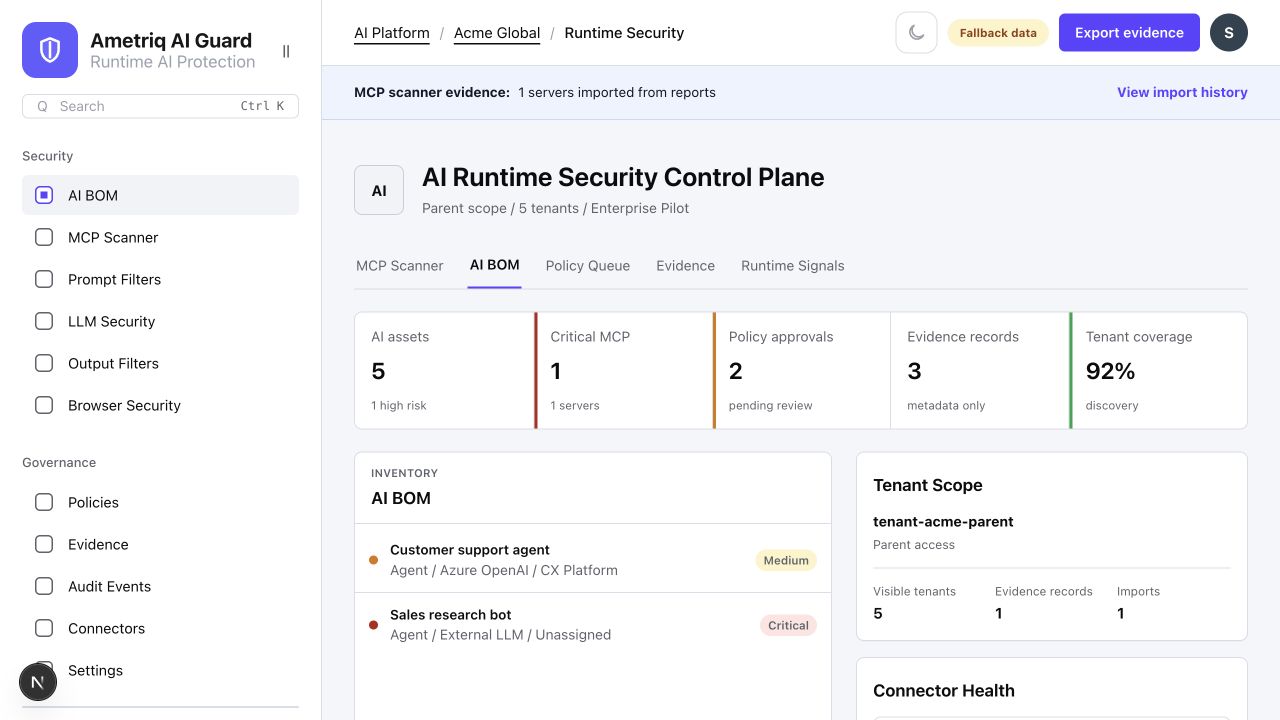
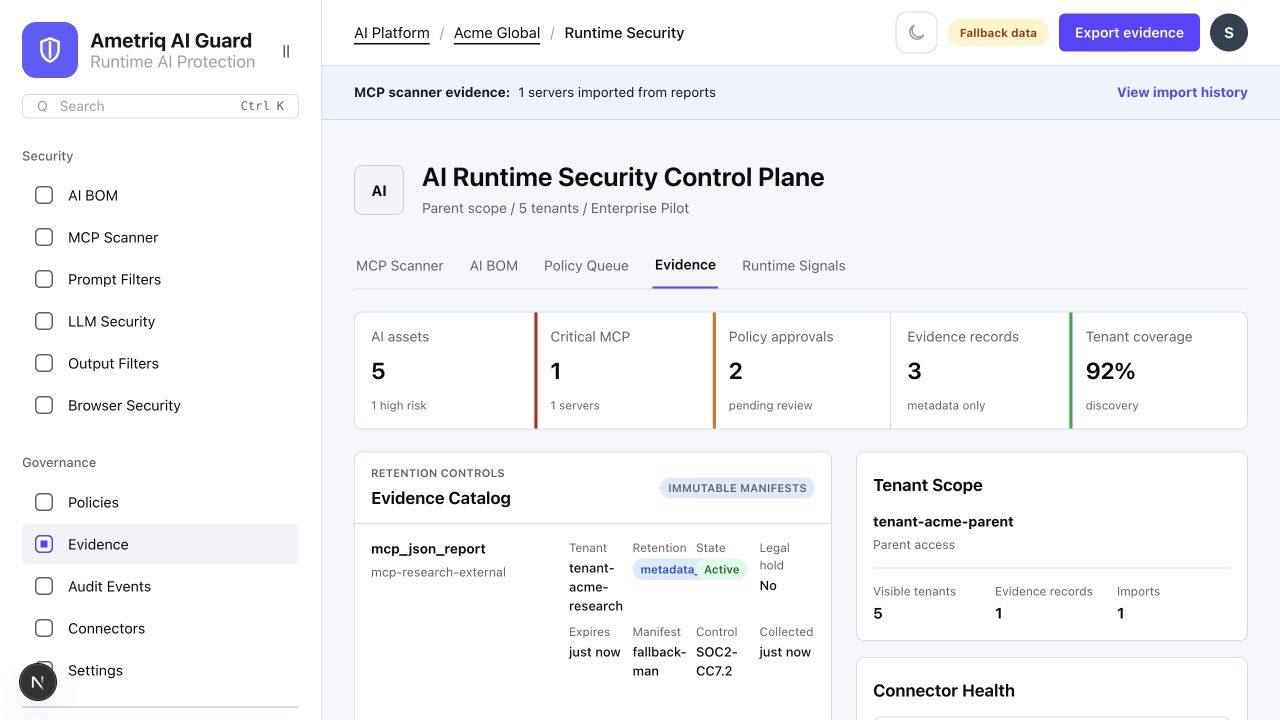
Every prompt, tool call and answer, checked before it runs.
AIGuard checks every prompt, tool call and answer your AI apps and agents produce, blocks or holds the risky ones for a person, and records every decision.
Runtime control plane
AI inventoryAudit evidence
ALLOWsupport-copilot · summarize ticket #4821BLOCKrag-search · injection in retrieved contextAUDITops-agent · mcp · db.execute DELETE held for approvalBLOCKhr-assistant · PII redacted from outputALLOWdev-copilot · mcp · github.read_file in scopeALLOWsales-assistant · CRM lookup, tenant verifiedAUDITfinance-agent · mcp · payments.refund above limitBLOCKkb-chatbot · system prompt override attemptALLOWsupport-copilot · summarize ticket #4821BLOCKrag-search · injection in retrieved contextAUDITops-agent · mcp · db.execute DELETE held for approvalBLOCKhr-assistant · PII redacted from outputALLOWdev-copilot · mcp · github.read_file in scopeALLOWsales-assistant · CRM lookup, tenant verifiedAUDITfinance-agent · mcp · payments.refund above limitBLOCKkb-chatbot · system prompt override attempt
How it works
One check between your AI and your business.
Your apps don't change. AIGuard sits in the path every AI request already takes, and decides what is allowed to happen before it does.
1
Your AI app or agent
Sends a request or tries an action, as it does today.
2
AIGuard checks it
Against your policy: who is asking, what data is involved, what the action would do.
3
Allowed, blocked or held
Safe requests go straight through. Risky ones are blocked, or held until a person approves.
AllowedBlockedHeld for a person
4
Logged as evidence
Every decision is recorded with its reason, ready for your auditors.
Where it runs
As a service, or inside your own cloud account
See a decision happen
Allow, block or hold. Before the action runs.
Your app or agent calls /api/ai/evaluate before each model or tool step. AIGuard checks it against your policy, returns a decision, and writes the evidence.
AIGuard · /api/ai/evaluatesimulated
Incoming request
support-copilot
Summarize ticket #4821 for the account owner.
GATE
Decision
ALLOW
In policy. Tenant scope verified.
19:17:10ALLOWsupport-copilot summarize ticket
19:17:10BLOCKrag-search injection in context
19:17:10AUDITops-agent db.execute DELETE
What it does
Four controls on every AI request.
01Stops attempts to trick your AI
Prompt and context inspection
Blocks instructions hidden in user messages or retrieved documents before they reach the model.
02Keeps agents to their job
MCP and tool authorization
Each agent can only take the actions it is allowed to. Risky ones wait for a person.
03Keeps sensitive data out of answers
Output filtering and redaction
Personal and confidential data is masked before it leaves your systems, which lowers GDPR and DPDP exposure.
04Records every decision
Audit evidence
Every allow, block or hold is logged with the policy that applied, ready for your review board.
Product demo
See runtime decisions, inventory and evidence.
The AIGuard console shows which MCP servers and agents are risky, which AI apps you run, and the evidence behind every decision.
Runtime decisions, inventory and evidence
Try AIGuard on one AI workflow for two weeks.
Week 1 only watches and records. In week 2 you review real decisions and the evidence behind them.